Hackers are looking for weaknesses and, when found, they’ll pounce.
If any of the following resemble your practice, you are definitely in trouble.
1. You have higher than average employee turnover.
If you’re losing employees more than the norm than there may be a reason behind this – like lower than average pay, less than fabulous working conditions, etc. When employees leave they sometimes take data with them – usually inadvertently but sometimes on purpose to use with a competitor or other vengeful reasons. Re-address your employee concerns and do your best to limit turnover – you will reduce a chance of a hack that way
2. Your staff is remote and/or mobile.
When employees are moving around they are moving around with your data – it can be easily lost or stolen. If an employee or contractor is remote then they are connecting to your database through online services and these have a chance of being hacked. Work with an IT person to make sure you have strong data management and connection tools in place for these remote people and make sure they’re being monitored
3. You have no IT support.
Speaking of an IT (information technology) person: get one. Even the smallest of companies are exposed to a data hack. Paying someone to evaluate your risks, install software, monitor activity and keep things up to date is a critical and essential business cost – even the work is done monthly (it all depends on your size and activity)
4. You do not buy security software.
Subscribe to one of the great security applications like McAfee, Norton, Malwarebytes or Bitdefender. There are many others. These software applications are inexpensive, run quietly in the background of every device and are checking for malware, viruses, infected websites and other tools of the hacker. Make sure this software is always updated.
5. Your employees do not get trained.
Most security problems, particularly at small companies, are from employee-related errors – clicking on bad websites, opening up infected files, etc. Invest in a day of training a few times a year with a good IT security firm so that your employees are well aware of potential problems and can avoid doing dangerous stuff.
6. You have no procedures for securing data.
If you are handling health, financial or other personal information about your customers, and it gets stolen, you could have a big problem on your hands. Keeping this data in an unprotected place means that hackers are going to find it. If this is you, then you’re going to need procedures and policies around the safeguarding of confidential customer data. And after they’re written training will be required to ensure that your employees are complying.
7. Your computers and operating systems are old.
Thousands of computers around the world are still running older, out of date versions of Microsoft Windows. All hackers need is one vulnerable computer to attack and then can get on a network and wreak havoc. One of the best ways to avoid a hack is to ensure that all of your computers are running the most recent versions of Windows or iOS all the time. If a desktop or other device is too old to handle the new operating systems then buy a new one. The cost will pale in comparison to the cost you’ll incur if you’re hacked
8. You have no BYOD policy.
Are your employees allowed to bring their own devices (a BYOD policy) and use them for work? That’s what most companies do. Unfortunately, this can create security issues if they are not monitored. Many companies use remote management software to install company apps on their employees’ devices for a secure access while other companies issue their own devices to their employees which have been secured. So, what is your Bring Your Own Device policy? Every company must have one and every company must have an IT person monitoring those devices.
9. Password changes are not enforced.
Most people are pretty complacent with passwords – the most common one, if you can believe it, is still “1234.” You must require a more complicated password for your employees to enter your network – a combination of letters, numbers and symbols – and this password should be required to be changed every month or two. That way passwords are more difficult to hack and hackers may move on to another easier target.
It’s unfortunate, but even in today’s era of two-factor authentication and hyper-alert security, we still hear stories of physicians being defrauded by their employees. To help protect yourself from financial fraud, consider adopting these five approaches in your practice.
1) Cross-Train Your Employees
The most common place for fraud to occur is in the back office of small businesses where only one person handles the cash and books. Train more than one person on the cash conversion cycle. Rotate people through the various processes, too, so that no single person operates in a silo. When multiple people know the process, they can check each other’s work for mistakes and anomalies. Cross-training employees helps to create an open and transparent environment. It also reduces the chance of theft by assuring no one person wields too much power. Ultimately, it would be best if you also knew the process, so you can be an effective leader and fiscally responsible business owner
Here’s some of the big trends Iconic believes you’ll be seeing a lot more of in 2022:
1. Companies will invest more in cybersecurity insurance than ever before.
2. Cloud-based desktop software like Microsoft’s Cloud PC will grow in popularity.
3. Companies of all sizes will rely on SIEM cybersecurity defenses.
4. Mobile devices will become a bigger target for hackers.
With more employees than ever working remotely, they’re more likely to use poorly protected cell phones and computers on unsecured wifi. According to Digital Information World, 40 percent of mobile phones are prone to attack, and in need of better authentications and cybersecurity software.
5. AI-enabled cybersecurity software will help companies mitigate network threats in their networks, and the Internet of Things.
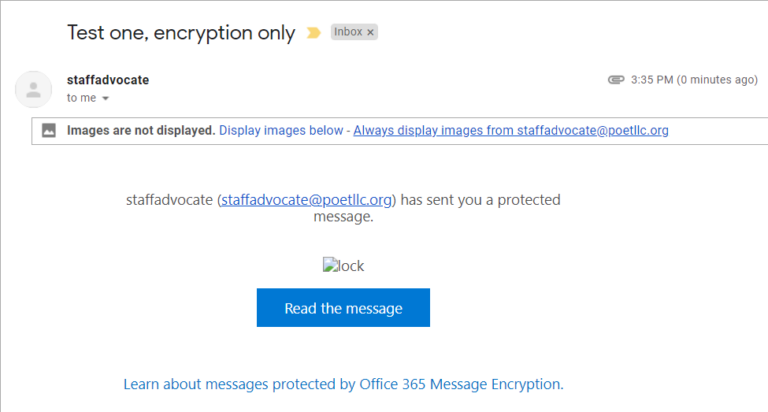
Make Sure email is a part of your cybersecurity stategy.
Email archiving is an automated process for preserving and protecting all inbound and outbound email messages (as well as attachments and metadata) so they can be accessed later. In other words, email archiving is storing emails and making them searchable.
Email archiving providers take this burden off organizations by storing emails on their servers while making them accessible to designated administrators in the organization. This is different than simply creating an email data backup. Data backups do not allow searching, so if a particular email needs to be found, it might take weeks for you to find it
Rachel V. Rose, JD, MBA January 13, 2020 Health IT, Pearls, Practice Management According to the National Institute for Standards and Technology (“NIST”), phishing is defined as “[a] technique for attempting to acquire sensitive data, such as bank account numbers, through a fraudulent solicitation in email or on a web site, in which the perpetrator masquerades as a legitimate business or reputable person.” Often times, phishing attacks, especially those executed through email and unsecure websites, lead to the deployment of ransomware.
To view the entire article check out “Security” under the “Compliance” File.

 Reload document
 Open in new tab
Recent Comments